Geehy has always prioritized product and user data security. To meet the requirements of the EU Cyber Resilience Act (CRA), Geehy has officially launched a Coordinated Vulnerability Disclosure (CVD) platform. It provides customers and partners with a secure, standardized, and transparent way to report vulnerabilities, helping device manufacturers meet compliance requirements for products sold overseas.
Understanding the CRA and the CVD Platform
What is the CRA?
The CRA (Cyber Resilience Act) is a legally binding EU cybersecurity regulation covering hardware and software products that connect directly or indirectly to networks. It requires manufacturers to manage cybersecurity throughout the entire product lifecycle, including secure-by-design development, vulnerability management, security updates, and security incident reporting.
What is a CVD platform?
Coordinated Vulnerability Disclosure (CVD) is a vulnerability-handling mechanism explicitly required by the CRA.
Geehy's CVD platform is designed to establish a standardized, closed-loop process for receiving, handling, and disclosing vulnerabilities. Its core capabilities include:
• Provides a secure and trusted channel for reporting vulnerabilities, including anonymous submissions;
• Standardizes the processes for receiving, verifying, assessing, remediating, and disclosing vulnerabilities;
• Keeps vulnerability information confidential until patches are released, helping prevent malicious exploitation;
• Maintains complete vulnerability-handling records to support CRA audits and help downstream manufacturers demonstrate compliance.
Geehy's CVD Product Coverage
Multiple Geehy APM32 MCU products now support security vulnerability reports submitted through the CVD platform. The platform accepts reports concerning security issues in the relevant chip hardware, official firmware, bootloaders, SDKs, and official reference code, helping strengthen the cybersecurity foundation of APM32 MCU products.
| Series | Part No. |
| Cortex-M0+ | APM32F091、APM32F072 APM32F051、APM32E030 APM32F030、APM32F003 |
| Cortex-M3 | APM32E103、APM32F103 APM32F107、APM32F105 |
| Cortex-M4F | APM32F427、APM32F425 APM32F417、APM32F415 APM32F407、APM32F405 APM32F465、APM32F411 APM32F403、APM32F402 |
Note: Customer-developed application code based on Geehy chips is outside the scope of the chip manufacturer's CVD platform. Customers may contact Geehy for guidance if needed.
Geehy's CRA Commitments and Practices
To meet the requirements of the EU CRA, Geehy fulfills its responsibilities as a semiconductor manufacturer through the following commitments:
1. Establishing a dedicated vulnerability reporting channel: Geehy has launched a publicly accessible CVD platform with clear reporting procedures and contact information.
2. Publishing an official CVD policy: Geehy publicly provides comprehensive coordinated vulnerability disclosure rules, clearly defining the scope of accepted reports, handling procedures, and safe harbor provisions.
3. Collaborating efficiently with security researchers: Geehy will acknowledge receipt of a vulnerability report within 48 hours and maintain open communication throughout the process.
4. Providing security updates throughout the product lifecycle: During the officially stated support period, Geehy will remediate vulnerabilities and provide firmware patches, SDK updates, or risk-mitigation solutions.
5. Conducting coordinated public disclosure: Once a remediation plan is ready, Geehy will publish a security advisory containing vulnerability details, affected versions, and recommended measures.
6. Providing supporting compliance materials: Geehy will provide customers with security manuals and risk-related documentation to support their CRA conformity assessments.
Geehy CVD Platform and Contact Information
Scan the QR code or visit the website below to access the Geehy CVD platform, review the complete CVD policy and safe harbor statement, and submit vulnerability reports directly. You may also contact Geehy's security team at fae@geehy.com.
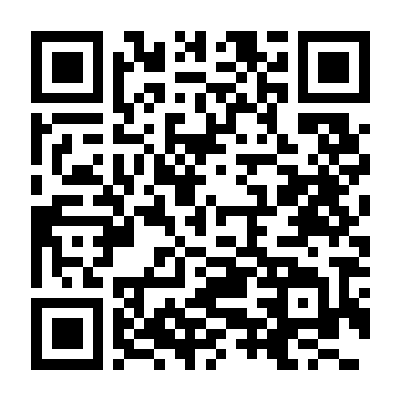
https://geehy.cvd.xa-sec.com/
Conclusion
As cybersecurity regulations in overseas markets become increasingly stringent, chip-level security has become a critical consideration for embedded products entering international markets. Geehy will continue to comply with international cybersecurity regulations, including the CRA, while continuously improving its product security and vulnerability response systems. By strengthening security across chip hardware, firmware, and the SDK software ecosystem, Geehy aims to help customers successfully bring their products to global markets.